

Security Leadership
Fractional CISO and security leadership: building a security program, hiring the right security leader, and what boards and executives should own.
Guides
-
· Jon Rose · 5 min read
Security Requirements by Industry: Healthcare, Fintech, and General B2B Compared
Healthcare, fintech, AI, general B2B: each industry has different security requirements. Here's what to expect.
-
· Jon Rose · 4 min read
What to Do When Your Security Team Can't Adapt to Business Changes
When business changes faster than your security program, the gap becomes dangerous. Learn when interim CISO leadership makes sense.
-
· Jon Rose · 5 min read
Compliance Is Not Security (And Security Is Not Compliance)
Passing audits and being secure are not the same thing. Here's the difference between a compliance program and a security program.
-
· Jon Rose · 4 min read
What Security Decisions Should a CEO Make? The Ones You Can't Outsource
Some security decisions require executive judgment. Here's what you can outsource to your CISO and what you can't.
-
· Jon Rose · 5 min read
Business Email Compromise: The Most Common Breach We See (And What to Do About It)
BEC is the most common breach we see. Here's the pattern, why it happens, and what prevention actually works.
-
· Jon Rose · 5 min read
How to Answer Security Questionnaires Without Killing Your Enterprise Deals
Security questionnaires stall enterprise deals when answers are vague or inconsistent. Learn how to build a response process that closes deals faster.
-
· Jon Rose · 5 min read
How to Hire a CISO When You're Not a Security Expert
Most companies hire a CISO wrong because they don't understand the role. How to evaluate candidates, set expectations, and avoid the common mistakes.
-
· Jon Rose · 4 min read
Security Requirements for AI Startups: What Investors and Enterprise Customers Actually Expect
AI startups face compressed timelines for enterprise sales. Here's what investors and customers actually expect from your security program.
-
· Jon Rose · 4 min read
SOC 2 vs ISO 27001: Which First?
SOC 2 vs ISO 27001: your market tells you which certification you need. Here's how to decide and when to pursue each.
-
· Jon Rose · 7 min read
How Much Should a Startup Spend on Security? A Budget Breakdown
Real security budget breakdown: MDR, endpoint, cloud posture, compliance, and more. What mid-market companies actually spend.
-
· Jon Rose · 4 min read
Should Your First Security Hire Be a CISO or Engineer?
The first security hire decision shapes your program. For most mid-market companies: fractional CISO plus full-time engineer.
-
· Jon Rose · 5 min read
How to Build a Security Program from Scratch: The First 90 Days
The first 90 days of a security program: assess, design, align, execute. Here's what actually gets done and in what order.
-
· Jon Rose · 6 min read
Security Quick Wins: What Gets Fixed in the First Two Weeks
What gets fixed in the first two weeks of a security program? File sharing, dead cloud resources, offboarding gaps, and more.
-
· Jon Rose · 3 min read
The Real Cost of Not Having Security Leadership
Not having a CISO costs more than you think: time tax on other functions, delayed deals, and incident response chaos. Here's what it actually costs.
-
· Jon Rose · 4 min read
Does My Startup Need a CISO? Signs You've Outgrown DIY Security
B2B startups hit a wall when security questionnaires kill deals. Learn the signs you need dedicated security leadership.
-
· Brett Wilson · 4 min read
The vCISO Dividend: Why Fractional Security Leadership is Gaining Momentum
The vCISO Dividend: Why Fractional Security Leadership is Gaining Momentum
-
· Brett Wilson · 5 min read
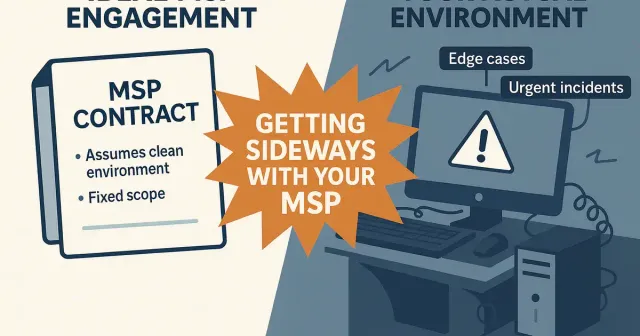
Why Do Fractional CISOs Get Sideways With Your MSP?
Learn why MSP relationships break down, how poor service fit harms security posture, and what virtual CISOs uncover during IT and security assessments.
-
· Brett Wilson · 3 min read
A Tale of Two Security Programs and Two Different Trajectories
Two companies, two CISOs, two very different outcomes: how culture, leadership, and follow-through define the real strength of a security program.
-
· Brett Wilson · 3 min read
Slay Internal Uncertainty With Effective AI Governance
AI adoption without governance is driving up costs and risks; securing measurable ROI requires stronger oversight and control.
-
· Jon Rose · 4 min read
SOC 2 Won’t Close the Deal. Customer Trust Will
SOC 2 compliance isn't enough; building and maintaining a robust security program is key to earning and sustaining customer trust.
-
· Jon Rose · 2 min read
Security Isn’t a Department, It’s How You Operate
Rather than isolating security to one department, integrate security into daily operations to ensure an effective and sustainable security posture.
-
· Jon Rose · 4 min read
The Real Hidden Costs of a Data Breach
Explore the hidden costs of data breaches beyond financial losses, including productivity hits, employee burnout, and strained customer communication.
-
· Jon Rose · 2 min read
Policies Without Culture Are Just PDFs
Effective security needs a strong culture, cross-functional alignment, and integration with business objectives, not just policies on paper.
-
· Jon Rose · 3 min read
When Hiring a Full-Time CISO Is Too Much
Why hiring a full-time CISO too soon can stall a growth-stage company, and how fractional security leadership builds the foundation first.
-
· Jon Rose · 4 min read
Hiring a CISO Won’t Magically Fix Security. Create Executive Alignment First.
Appointing an experienced security leader without first agreeing on security objectives, risks, and tolerances rarely solves the problem, and can make it worse.
-
· Jon Rose · 1 min read
Here are the 4 most thought-provoking cyber security questions the National Association of Corporate Directors (NACD) wants your board to ask you.
We frequently ask these questions to executive teams to gauge the maturity of the cybersecurity program. Can you answer these?
-
· Jon Rose · 4 min read
The vCISO Dividend
Most executive leadership teams today are uncomfortably aware of the need for a strong information security posture, but not all are able to ensure it.
-
· Jon Rose · 2 min read
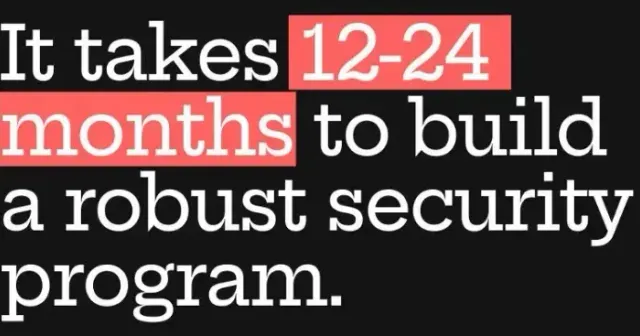
It takes 12 to 24 months to build a robust security program
I’ve watched this unfold a million times. The executive team is laser-focused on growth, while security is pushed aside.
-
· Jon Rose · 4 min read
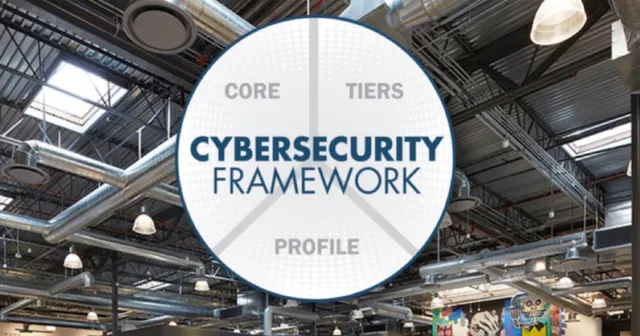
Building a Strong Security Program Using the NIST Cybersecurity Framework
Security assessments are ubiquitous, but they vary widely in their objectives and usefulness to your organization.
-
· Jon Rose · 4 min read
Accelerate Growth with a Strong Security Posture
Bidding on new business means vendor security questionnaires and proving alignment with customer security programs. A strong security posture speeds that up.
Practical security guidance for growing companies: building security programs, passing customer security reviews, and making smart security decisions.