

Here are the 4 most thought-provoking cyber security questions the National Association of Corporate Directors (NACD) wants your board to ask you.
By Jon Rose, Founder & Managing Partner · · Updated · 1 min read
We frequently ask these questions to executive teams to gauge the maturity of the cybersecurity program.
Can you answer these questions?
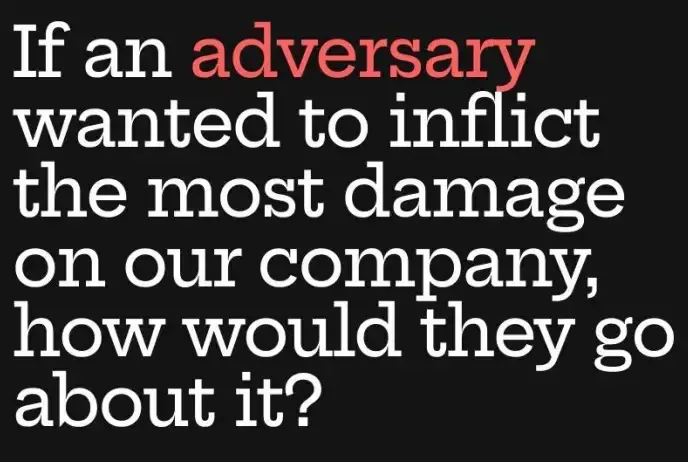
If an adversary wanted to inflict the most damage on our company, how would they go about it? If you don’t know your vulnerabilities, your adversaries will find them for you. This question forces CTOs to think like the adversary…
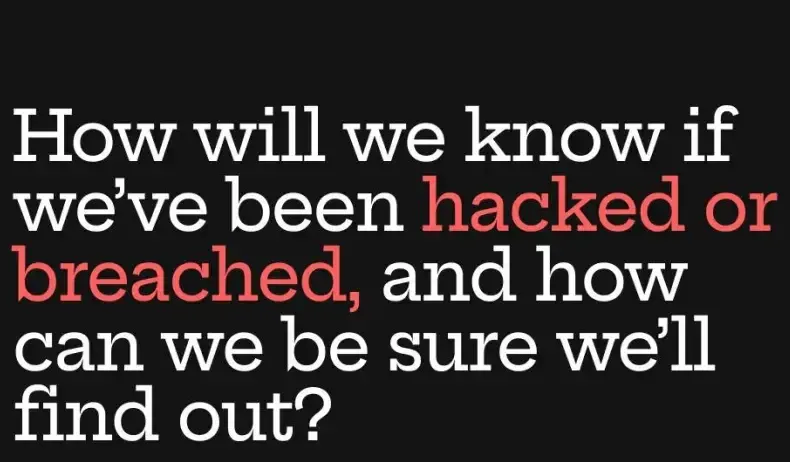 How will you know if you have been hacked?
Do you have confidence in your detection and response capabilities? Are there blindspots?
This is designed to get insight into the maturity and coverage of security monitoring.
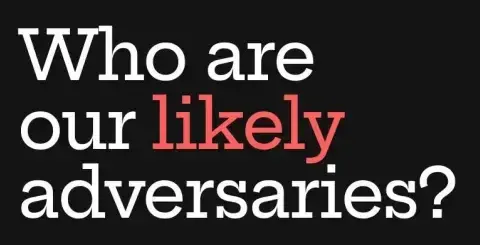
Who would target you? What’s their motivation?
Different attackers have different tactics, techniques, and procedures for attacks. Knowing your threat actors helps guide security investment and protective controls.
What’s the definition of Material for your business? Typically this is defined in financial terms.
Do you have a clear escalation process?
Run it by a CISO.
30 minutes. No pitch. Talk to a practicing CISO.
Talk to a CISOAbout IOmergent
IOmergent is the operating CISO for growth-stage companies. Founded in 2021 by Jon Rose and Brett Wilson, we provide fractional CISO (vCISO) services and Managed Cloud Security to SaaS, fintech and healthtech companies. Our team includes 25+ CISOs, and every CISO on our team has led security programs in-house. We have delivered 100+ engagements for 45+ companies. Fractional CISO engagements typically run $8,000 to $25,000 per month, and most engagements start within 2 weeks. More about us